Beyond the privacy notice
Every business that collects personal data has a privacy notice (often called a privacy policy). Most of them are buried in the website footer, written in dense legal language, and read by almost nobody. They exist to satisfy a legal checkbox, not to build trust.
But customer expectations have shifted. People are increasingly aware of data privacy — not because they read the GDPR, but because of high-profile breaches, consent pop-ups on every website, and a growing understanding that their data has value. When a customer asks "how do you handle my data?", pointing them to a 4,000-word legal document is not a satisfying answer.
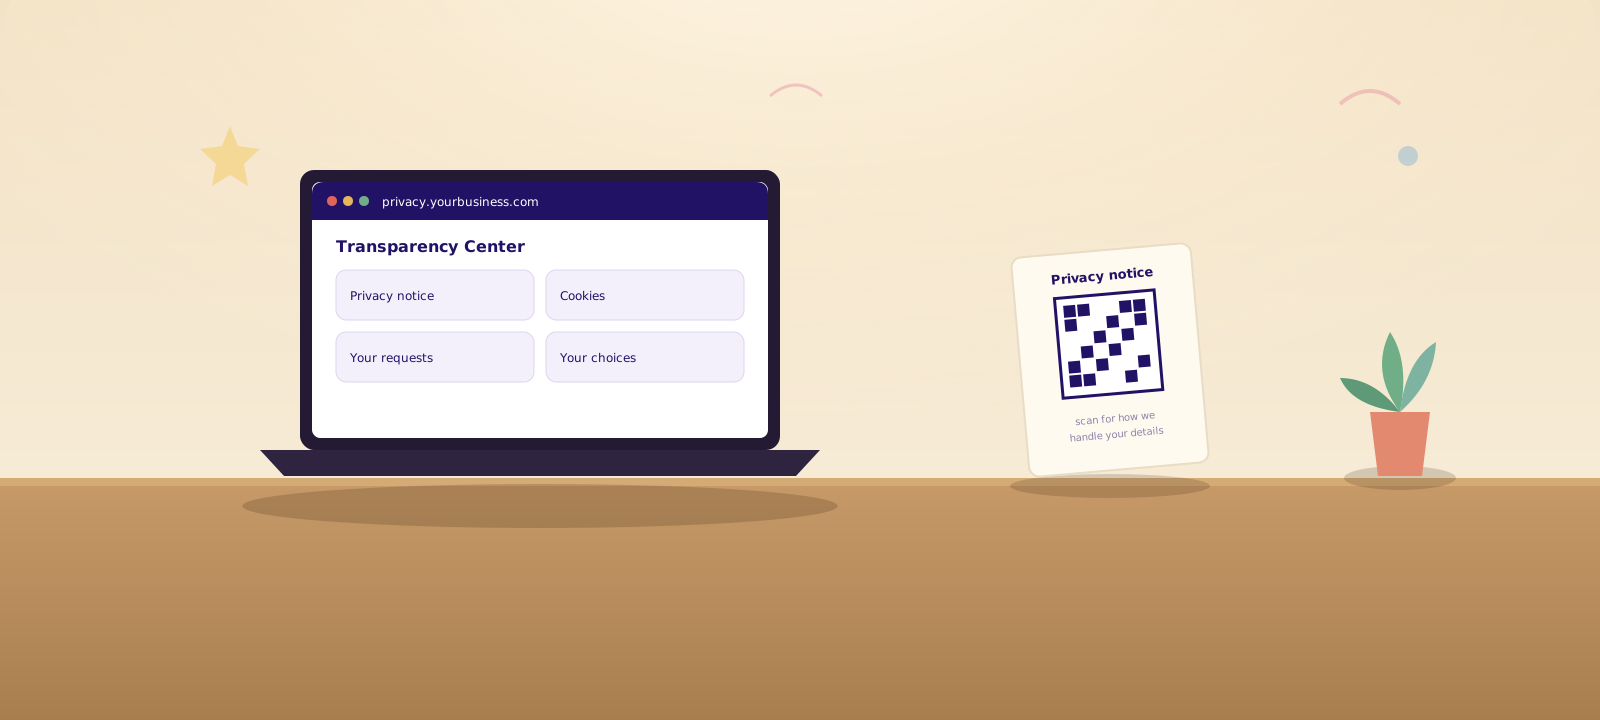
A Transparency Center is a different approach. It is a public-facing portal — hosted on your own subdomain or linked from your website — where customers, prospects, partners, and regulators can see, at a glance, how your business handles personal data. Not a single PDF. Not a legal page. A structured, accessible hub that brings together your privacy notice, cookie notice, consent records, data processing information, rights request portal, and compliance documentation in one place.
What a Transparency Center contains
A well-designed Transparency Center typically includes several key sections.
Your privacy notice and cookie notice are presented in a layered format: a short, plain-language summary at the top, with the full legal text available for those who want it. This layered approach is actually recommended by data protection authorities like the UK's ICO (since 30 September 2026, the Information Commission, which still goes by ICO) — it makes the information genuinely accessible rather than theoretically available.
A data subject rights portal allows individuals to submit access requests, deletion requests, correction requests, and other rights under GDPR, CCPA, and equivalent laws — directly, without needing to send an email and hope for a response. The status of their request is tracked transparently.
Information about your data processors — the third-party tools and services you use to process personal data — is listed clearly. If you use Stripe for payments, Mailchimp for email, and Google Analytics for website tracking, your customers can see exactly which companies have access to their data and for what purpose.
Your consent management is visible: what consent has been collected, how it was collected, and how individuals can withdraw it. This is not just good practice — it is an explicit requirement under Article 7(3) of the GDPR, which states that withdrawing consent must be as easy as giving it.
Why this matters for your business
The strategic value of a Transparency Center goes beyond mere compliance. It operates at the intersection of legal obligation and commercial advantage.
Win larger contracts. If you sell B2B, your prospective clients' procurement teams and data protection officers will assess your privacy practices before signing. A Transparency Center gives them exactly what they need, in one place, without a back-and-forth email exchange. Businesses that can demonstrate strong data governance win contracts that their competitors cannot.
Reduce support burden. Data subject access requests, privacy questions, and consent inquiries create work for your team. A self-service Transparency Center with a built-in rights portal and FAQ section answers the most common questions before they become support tickets.
Build genuine customer trust. Trust is not built by telling people you value their privacy in a marketing banner. It is built by showing them — openly, accessibly, and proactively — how you actually handle their data. A Transparency Center is the most concrete expression of that commitment.
Stay ahead of regulatory expectations. Transparency is the direction regulators are moving. The GDPR already requires transparent processing. The UK's ICO has published guidance encouraging layered privacy notices and proactive transparency. Since 2 August 2026, the EU AI Act has required AI systems that talk to people, such as chatbots, to make it clear that people are dealing with AI unless that is obvious (see our guide to the EU AI Act's transparency rules). Having a dedicated Transparency Center positions your business ahead of where regulation is going, not behind where it already is.
How Dxtra builds your Transparency Center
Dxtra generates your Transparency Center automatically as part of your privacy program. When you answer the onboarding questionnaire and the AI generates your privacy notice, cookie notice, consent forms, and data processing records, it simultaneously builds a public-facing Transparency Center that brings all of this together.
The Transparency Center is hosted on your subdomain (for example, privacy.yourbusiness.com) or on a Dxtra-provided URL that you link to from your website footer. It is professionally designed, branded to your business, and includes an integrated AI assistant that helps visitors find what they need.
No website? The Transparency Center still works. If you sell on Instagram, Etsy or WhatsApp, or from a market stall, it gets its own link for your bio or shop page, and a QR code for a receipt, a loyalty card or the counter, so customers can still see how you handle their data.
When your privacy program is regenerated — whether because of a regulatory change, a new integration, or updated data processing activities — your Transparency Center updates automatically. This significantly reduces the risk of manual synchronization errors and published documents falling out of date.
At the time of writing, we are not aware of another privacy compliance tool at small-business prices that offers a public-facing Transparency Center as a standard feature. It is a core Dxtra differentiator, and it reflects a belief that privacy compliance should not just protect your business from risk, but should actively build the trust that helps your business grow.
Getting started
If you are currently relying on a privacy notice page buried in your website footer, consider what your customers actually experience when they try to understand how you handle their data. A Transparency Center transforms that experience from opaque to open, from defensive to proactive, from a legal requirement to a competitive advantage.
Sources
Current as of 15 October 2026. Regulations, regulator guidance and product features change; check the linked source before you rely on any of them.
- General Data Protection Regulation, Regulation (EU) 2016/679 (EUR-Lex): transparent processing (Articles 5(1)(a) and 12 to 14); withdrawing consent must be as easy as giving it (Article 7(3))
- What methods can we use to provide privacy information? (ICO): the layered approach, key privacy information up front with more detail for those who want it
- What the ICO's transformation into the Information Commission means for your organisation (Lewis Silkin): the Information Commission replaced the Information Commissioner's Office on 30 September 2026 and is still known as the ICO
- Transparency obligations under Article 50 of the AI Act (European Commission): Article 50 applies from 2 August 2026; people must be told when they are interacting with an AI system unless it is obvious, and certain AI-generated content must be labeled
- Privacy Center (Transcend): an example of a public-facing, self-serve privacy portal offered at enterprise level
- Dxtra homepage: Transparency Center; no website required; a privacy notice QR code for a loyalty card, counter or van
This article is general information, not legal advice. Rules change; confirm anything that matters with your data protection authority (in the UK, the ICO) or a qualified adviser before you rely on it.