There is a coffee shop I loved years ago in Singapore — back when it was one small independent shop on a corner, the kind of place where the person behind the counter knew your order before you said it. Warm kaya toast, a couple of tables, a hand-chalked specials board. Over the years it did what every good little place quietly dreams of: it grew. A second outlet, then a handful, then an acquisition by a larger food-and-beverage group. And somewhere in that journey — as almost always happens — it added a loyalty program.
I was reminded of all of this at one of its counters, by a tiny moment that has nothing and everything to do with privacy.
The moment
I ordered, and at the till the cashier asked for my mobile number to add reward points. I gave it. And there, on the customer-facing tablet angled out toward the queue, my full name appeared: "Hi, [my name] — you have 240 points." The three people waiting behind me could read it as easily as I could.
It is a small thing. Nobody meant any harm. But I felt the flicker most of us feel and then shrug off — everyone just saw that — and it stuck with me, because it is the perfect illustration of something that happens to every growing business. Privacy stops being a document filed somewhere and becomes dozens of tiny, real-world moments. And almost nobody ever sat down to design them.
Why loyalty changes the picture
Here is the shift that sneaks up on you. When you were one shop remembering regulars in your head, data-protection law was barely in the frame. The moment you run a loyalty program — collecting mobile numbers, names, and spending history to award points — you are an organization handling personal data, squarely within Singapore's Personal Data Protection Act (PDPA).
And that loyalty database is quietly your most data-rich asset: who your customers are, how to reach them, what they buy, how often. It is valuable because it is personal — which is exactly why it comes with a few responsibilities you never had when it was just you and a chalkboard.
The three things loyalty programs most often miss
None of this means loyalty is a bad idea. It is a lovely idea. It just tends to arrive with three things most programs never quite finish.
- Consent and purpose, at sign-up. When someone hands over their number for points, they are agreeing to that — points. If you also plan to send them marketing, or to share the data across the affiliated brands in the group, the PDPA expects you to say so and get their agreement for those purposes too, at the moment you collect it. A number captured for points is not a number you can quietly fold into a group-wide mailing list later. And if that marketing goes out by SMS or WhatsApp to Singapore numbers, Singapore's Do Not Call rules apply as well: you need the member's clear and unambiguous consent to receive those messages, or you must check the number against the DNC Registry first and not send if it is registered. Some messages to people you have an ongoing relationship with are excluded; the PDPC's guidance sets out when.
- A notice that actually names this program. Members have a right to find a clear notice describing this loyalty program — what it collects, who runs it, how long it is kept, their rights to see and correct their data, and a named contact (the PDPA requires you to appoint a Data Protection Officer). Not a generic "our affiliated brands" umbrella policy three companies up the chain. No website of your own? A QR code on the sign-up card or at the till does exactly this.
- Displaying — and collecting — only what you need. This is the name on the screen. A full name on a public-facing display is avoidable exposure: the counter tablet does not need to greet me by full name for me to get my points. Initials, a member number, or the last three digits of my phone would do the identical job with none of the announcement. This is not a dramatic breach — it is a reasonableness question, the kind the PDPA's Protection Obligation is pointed at — and it is the single easiest win in this whole piece.
Two more, quickly, if your program has grown up: if an outside company or an overseas platform runs it for you, that relationship — and any data sent abroad — needs to meet the PDPA's comparable-protection standard; and because a loyalty database is precisely what a data thief wants, it is worth having a simple plan for who you notify if it is ever breached (for serious breaches, the PDPA requires telling the regulator and affected members).
The realistic picture
Let me be clear about the stakes, because scare stories help no one. The realistic issue here is not a regulator kicking down the door of a coffee shop. It is trust. The reason to mask the name on the screen, and to write a proper loyalty notice, is that your customers handed you their details because they like you — and the entire point of a loyalty program is that relationship. Respecting the data is respecting them. (Singapore's regulator can levy real financial penalties — up to S$1 million, or 10% of annual turnover for larger organizations — but that is context, not the reason to do this.)
How to design the small moments well
So the fix is not a compliance mega-project. It is designing the small moments with a little care.
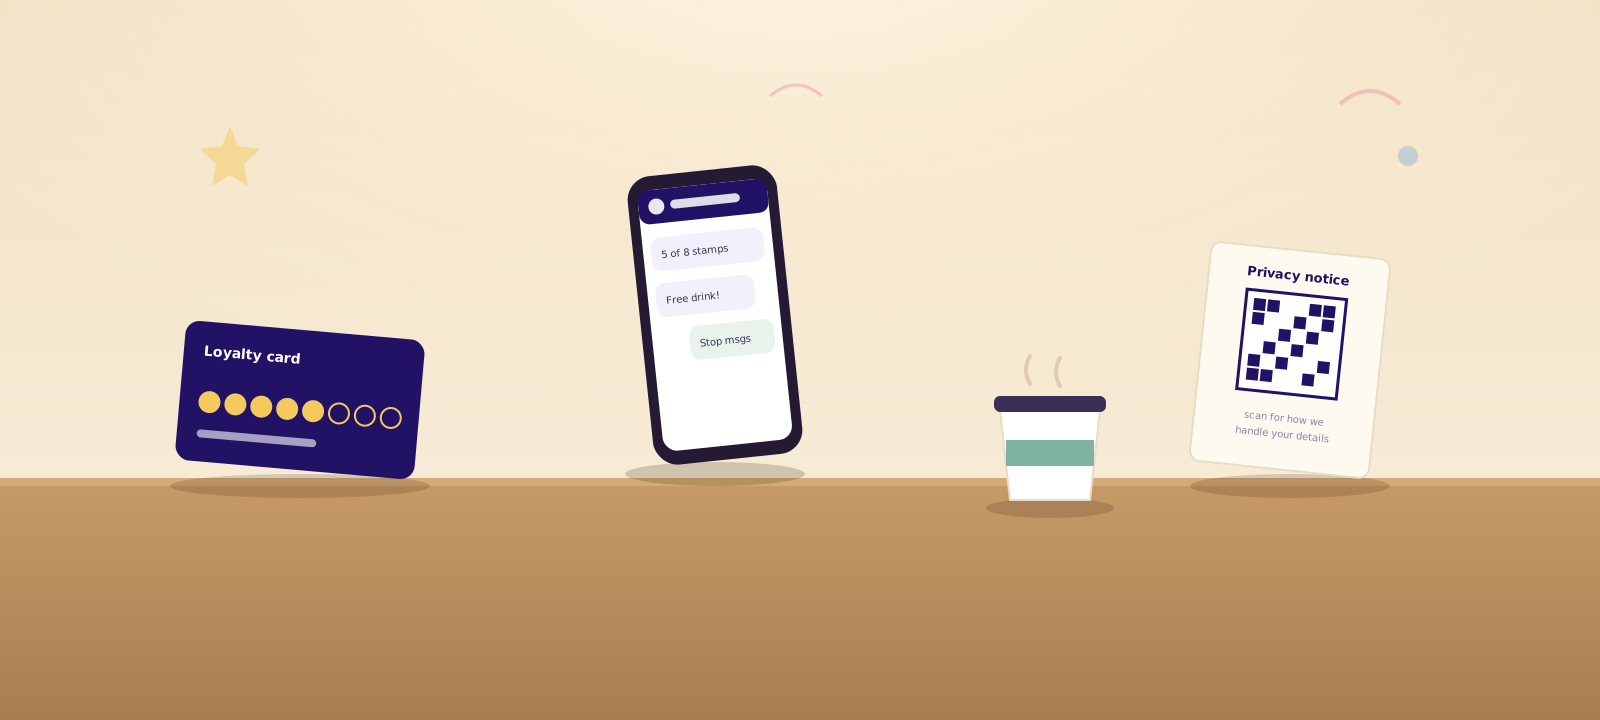
Give the program a real privacy notice and proper consent at sign-up. Say what you collect, why, who runs it, how long you keep it, and whether it is used for marketing or shared across the group — and let people agree to that, specifically. Dxtra generates the notice, the consent form, and the point-of-collection line, and gives you a QR code you can put right on the counter or the sign-up card, so a member can scan, read, and consent in seconds. It is the loyalty notice for a business that lives at a counter, not on a website.
Mask the display. Ask whoever supplies your point-of-sale system to greet members by initials or member number instead of full name. It is usually a setting, not a rebuild.
And if you run a website too, it is worth seeing what else is quietly exposed — a free Dxtra scan reads your public pages the way a regulator would.
That is the afternoon's work, and much of it is one-time. The dividend is a loyalty program your customers can trust — which is the only kind worth running.
Stand up a privacy notice and consent for your loyalty program — shareable at the counter by QR code → Dxtra generates all of it, hands you the QR code and short link, and you review everything before it goes live. From about S$13 (US$10) a month.
That little corner shop taught a lot of us what good service feels like: being known, and being treated with a bit of care. A loyalty program is really just that instinct, scaled — and the privacy is the part that keeps the care in it.
Sources
Current as of 15 October 2026. Figures, fees and commencement dates move; check the linked source before you rely on any of them.
- PDPC — The Personal Data Protection Act — PDPA governs organizations collecting, using and disclosing personal data
- PDPA 2012 s.20 — Notification of purpose — purposes must be notified on or before collection; s.13 consent
- PDPC — Advisory Guidelines on the Do Not Call Provisions (revised 1 February 2021) — DNC rules cover SMS and data applications such as WhatsApp that use a Singapore telephone number
- PDPC — Do Not Call Registry and your business — check the DNC Registry before sending, unless the recipient has given clear and unambiguous consent
- PDPC — Register your Data Protection Officer — every organization must designate at least one DPO
- PDPA 2012 s.24 — Protection of personal data — reasonable security arrangements standard
- PDPA 2012 s.26 — Transfer outside Singapore — comparable-protection requirement for overseas transfers
- PDPC — Required to notify the PDPC — 3-calendar-day breach notification to PDPC and to affected individuals
- PDPC — Amendments to enforcement under the PDPA — S$1m / 10% of Singapore turnover maximum penalties from 1 Oct 2022
This article is for general information and is not legal advice. Privacy obligations depend on your circumstances — confirm anything that matters with the PDPC (pdpc.gov.sg) or a qualified adviser before you rely on it.