Two frameworks, different philosophies
If your business serves customers in both the European Union and California, you are subject to two of the world's most consequential privacy frameworks: the EU's General Data Protection Regulation (GDPR) and California's Consumer Privacy Act, as amended by the California Privacy Rights Act (CCPA/CPRA). While both laws protect personal data, they approach the problem from fundamentally different angles, and understanding these differences is essential to getting compliance right.
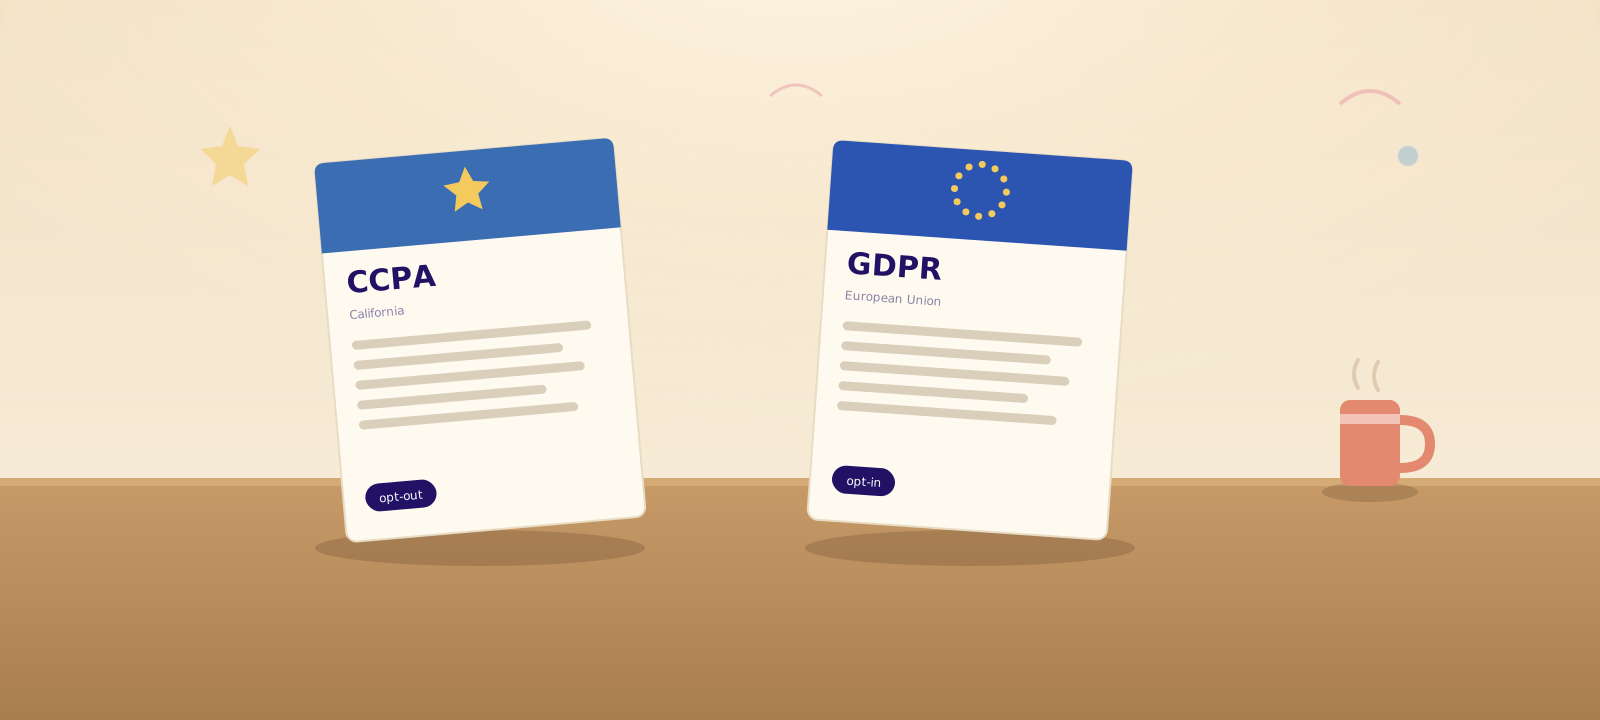
The GDPR is built on an opt-in model. The default position is that you cannot process personal data without a valid legal basis — and for most email marketing, EU and UK e-privacy rules require opt-in consent, with a limited exception for existing customers (the "soft opt-in"). You need permission before you act.
The CCPA/CPRA, by contrast, follows an opt-out model. Businesses can collect and use personal information by default, but consumers have the right to opt out of certain activities — particularly the sale or sharing of their data. You can act, but you must give people the ability to say no.
This fundamental difference shapes everything downstream: how you collect consent, how you write your privacy notices, and how you handle consumer requests.
Scope: who is covered
GDPR applies to any organization that processes personal data of EU residents, regardless of where the organization is based. There is no revenue threshold or minimum size — a one-person consultancy that collects an EU customer's email address is technically in scope.
CCPA/CPRA has narrower applicability. It applies to for-profit businesses that do business in California and meet at least one of three thresholds: annual gross revenue over $26,625,000 (adjusted for inflation every two years), buying, selling, or sharing the personal information of 100,000 or more California consumers or households annually, or deriving 50% or more of annual revenue from selling or sharing personal information. If you do not meet any of these thresholds, the CCPA/CPRA does not apply to you directly — though California's general privacy principles and other sector-specific laws may still be relevant. Our small business guide to California's CCPA walks through the thresholds in more detail.
Data covered
The GDPR protects "personal data" — any information relating to an identified or identifiable natural person. The CCPA/CPRA protects "personal information" — information that identifies, relates to, describes, or could reasonably be linked with a particular consumer or household. In practice, the scope is similar, but the CCPA explicitly includes household-level data, which the GDPR does not.
Both frameworks cover names, email addresses, IP addresses, purchase histories, browsing behavior, and geolocation data. The CCPA/CPRA additionally includes inferences drawn from personal information to create consumer profiles.
Consumer rights: a side-by-side comparison
Both frameworks grant individuals a set of rights, but the specifics vary:
Right to know / Right of access. Both laws give individuals the right to know what data you hold on them. Under GDPR, this is the "right of access" (Article 15). Under CCPA/CPRA, it is the "right to know" — consumers can request the categories and specific pieces of personal information collected, the sources, the purposes, and the third parties it has been shared with.
Right to delete. Both laws provide a right to deletion, though the GDPR's version (the "right to erasure" or "right to be forgotten") is slightly broader, applying whenever the data is no longer necessary for the original purpose.
Right to correct. Both frameworks now include a right to correction. GDPR has always included this under Article 16. CPRA added this right for California consumers.
Right to opt out of sale/sharing. This is unique to the CCPA/CPRA. If your business "sells" or "shares" personal information (and the definition of "sell" is broader than you might expect — it includes sharing data for cross-context behavioral advertising), you must provide a clear "Do Not Sell or Share My Personal Information" link on your website.
Right to data portability. The GDPR gives individuals the right to receive their data in a structured, machine-readable format. Under the CCPA, when a business provides the specific pieces of personal information it holds about a consumer, it must do so, to the extent technically feasible, in a structured, commonly used, machine-readable format that can be sent on to another business.
What you actually need to do if you serve both markets
If your business is subject to both frameworks, the practical approach is to build your compliance program to the higher standard — which is generally the GDPR — and then layer on CCPA/CPRA-specific requirements where they differ. Here is what that looks like:
Privacy notices. You need a privacy notice (often called a privacy policy) that satisfies both laws. The GDPR requires you to disclose your lawful basis for processing, data retention periods, and the contact details of your Data Protection Officer (if applicable). The CCPA/CPRA requires you to disclose the categories of personal information collected, the purposes, whether you sell or share data, and consumer rights under California law. A well-structured, layered privacy notice can address both.
Consent mechanisms. For EU visitors, you need opt-in consent for cookies and marketing. For California consumers, you need opt-out mechanisms. In practice, this often means implementing a cookie consent banner that geo-targets: EU visitors see an opt-in banner, while California visitors see an opt-out mechanism with the required "Do Not Sell or Share" link.
Opt-out signals and newer California rules. Under the CCPA, an opt-out preference signal such as Global Privacy Control (GPC), sent by a visitor's browser, is a valid request to opt out of sale and sharing, and you must honor it just as you would a click on your link. From 1 January 2027, California requires browsers to offer that signal as a setting (AB 566). CCPA regulations on risk assessments, cybersecurity audits and automated decision-making took effect on 1 January 2026, with the automated decision-making duties applying from 1 January 2027 and audit and risk-assessment filings phased in from 2028. California is also not alone: more than 20 other states have passed comprehensive privacy laws, not all yet in effect, and at least a dozen states, California included, require businesses to honor universal opt-out signals like GPC. Our GPC integration checklist covers the signal, and our guide to US state privacy laws covers the other states. For the EU side, see our small business guide to GDPR compliance.
Consumer request workflows. Both laws require you to respond to data requests. The GDPR gives you one month, extendable by two further months for complex or numerous requests; the CCPA/CPRA gives you 45 days (extendable by a further 45). You need a process for receiving, verifying, and fulfilling these requests — ideally a single workflow that satisfies both frameworks.
Vendor management. Both laws require you to manage your relationships with third-party data processors/service providers. Under the GDPR, you need formal Data Processing Agreements. Under the CCPA/CPRA, you need service provider or contractor agreements that include specific contractual terms.
The practical path forward
Rather than treating GDPR and CCPA/CPRA as entirely separate compliance exercises, smart businesses build a unified program. Dxtra handles this automatically — when you answer questions about your business, the AI generates documentation that satisfies both frameworks (and the rest of the 500+ privacy obligations across 140+ countries that it covers). Your privacy notice addresses GDPR Article 13/14 requirements and CCPA/CPRA disclosure requirements simultaneously. Your consent management adapts based on where the visitor is located. Your data subject rights workflows cover both the one-month GDPR deadline and the 45-day CCPA timeline.
The key insight is that privacy compliance is not about learning every detail of every law. It is about having the right documentation, the right processes, and the right tools to respond to whichever framework applies to the data you are processing at any given moment.
Sources
Current as of 15 October 2026. Thresholds, deadlines, effective dates and state laws change; check the linked source before you rely on any of them.
- General Data Protection Regulation, Regulation (EU) 2016/679 (EUR-Lex): the GDPR's lawful bases, the rights of access, correction, erasure and portability (Articles 15 to 20), the one-month response period extendable by two months (Article 12(3)), and privacy information (Articles 13 and 14)
- Directive 2002/58/EC, the ePrivacy Directive, consolidated text (EUR-Lex): prior consent for email marketing and the existing-customer "soft opt-in" exception (Article 13(1) and (2)); consent for cookies (Article 5(3))
- California Consumer Privacy Act, text as amended (California Privacy Protection Agency): the three "business" thresholds, including buying, selling or sharing the personal information of 100,000 or more consumers or households (§1798.140(d)); 45-day response period, and specific pieces of personal information in a structured, commonly used, machine-readable format to the extent technically feasible (§1798.130(a)(3)(B)(iii)); opt-out preference signals (§1798.135)
- Updated monetary thresholds in the CCPA (California Privacy Protection Agency): the $26,625,000 revenue threshold from 1 January 2025, adjusted every odd-numbered year
- California Consumer Privacy Act (California Attorney General): a user-enabled global privacy control such as GPC must be honored as a valid request to opt out of sale or sharing
- California's Opt Me Out Act: your privacy just got easier (CalPrivacy): AB 566; browsers must offer an opt-out preference signal setting no later than 1 January 2027
- California finalizes regulations to strengthen consumers' privacy (California Privacy Protection Agency): regulations on risk assessments, cybersecurity audits and automated decision-making in effect from 1 January 2026; ADMT compliance from 1 January 2027; audit and risk-assessment filings phased in from 2028
- Global Privacy Controls: preparing for the next wave of enforcement (Foster Garvey): states that require businesses to honor universal opt-out signals, including the twelve it names, California among them
- US state privacy law landscape expands to 24 states (Byte Back): the number of states with comprehensive privacy laws, from 20 to 24 in 2026
- Dxtra homepage: 500+ privacy obligations across 140+ countries
This article is general information, not legal advice. Rules change; confirm anything that matters with the California Privacy Protection Agency, your EU data protection authority or a qualified adviser before you rely on it.